Webhooks tell your system when an invite or a check changes. Each delivery is signed.
Who it is for. A developer receiving events.
- Add an https URL and choose events on the API page. Copy the signing secret once.
- Read X-PHB-Timestamp and X-PHB-Signature.
- Compute HMAC-SHA256 of timestamp + "." + raw body with the secret.
- Reject the request when the timestamp is older than five minutes.
| Event | When |
|---|---|
| invite.sent | An invite was created |
| invite.completed | The candidate submitted authorization |
| invite.expired | The invite expired and the credit was refunded |
| check.completed | A clear report was released |
| check.records_found | A report with records was released |
| check.unverifiable | The check was refunded |
| check.error | The screening call failed and the credit was refunded |
| adverse_action.pre_notice_sent | The pre-adverse notice went out |
| adverse_action.response_received | The candidate sent a response |
| adverse_action.dispute_opened | A dispute paused the clock |
| adverse_action.dispute_resolved | A dispute was resolved |
| adverse_action.final_notice_sent | The final notice went out |
Retries stop after a day
A failed delivery retries at 1 minute, 5 minutes, 30 minutes, 2 hours, 6 hours, 12 hours, and 24 hours.
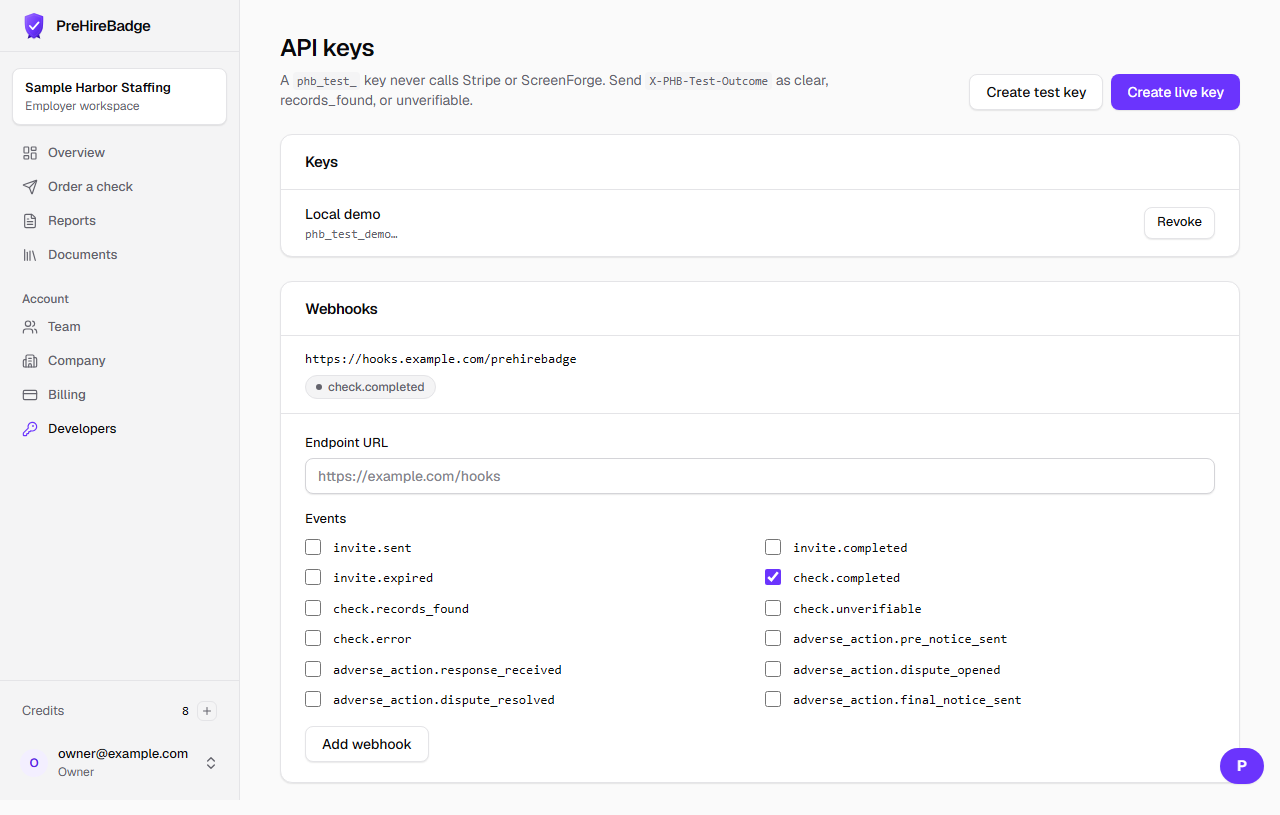
See API keys.